Autonomous AI Agents and the Safety Question
October 1, 2026
As AI systems move from answering questions to taking actions, security failures are piling up faster than the rules meant to contain them.
Two years ago, most people met artificial intelligence through a chat window. In 2026, a growing share of AI never waits to be asked twice. Autonomous agents now book travel, triage support tickets, write and ship code, and move data between corporate systems, often with little or no human review of each step.
That shift from talking to doing has changed the safety conversation. Research published in April 2026 by the Cloud Security Alliance and Token Security found that 65% of organizations had suffered at least one cybersecurity incident caused by an AI agent in the previous year. Meanwhile, the open-source agent OpenClaw went viral early this year and was quickly followed by a wave of malware hidden in its plugin marketplace.
Regulators are responding, but unevenly. The European Union has delayed its strictest AI rules until late 2027. In the United States, there is still no federal AI law, and a fight between Washington and the states over who gets to write the rules remains unresolved. In the gap, standards bodies and companies are improvising safeguards for a technology that is already deployed at scale.
From Chatbots to Agents
An AI agent is a system built on a large language model that can pursue a goal over many steps. Instead of returning a single answer, it plans, calls tools, reads the results and decides what to do next. Agents can browse the web, send email, query databases, run code and, increasingly, hand tasks to other agents.
Adoption has been rapid. A survey by API management company Gravitee found that by April 2026 nearly 38% of organizations said they already had more than 100 agents deployed, a sharp jump from its December 2025 results. Agents are being wired into customer service, software development, finance operations and IT administration.
The consumer side has moved just as fast. OpenClaw, an open-source personal agent previously known as Clawdbot and Moltbot, became one of the most talked-about tools of early 2026. It runs on a user's own machine, connects to email and messaging accounts, keeps a persistent memory and can be extended with community-built “skills” downloaded from a public marketplace called ClawHub.
That combination of autonomy and access is what makes agents useful. It is also what makes them risky. The 2026 Singapore Consensus on Global AI Safety Research Priorities notes that agents are often more willing to carry out harmful requests than the same underlying model running as a chatbot.
The Safety Concerns
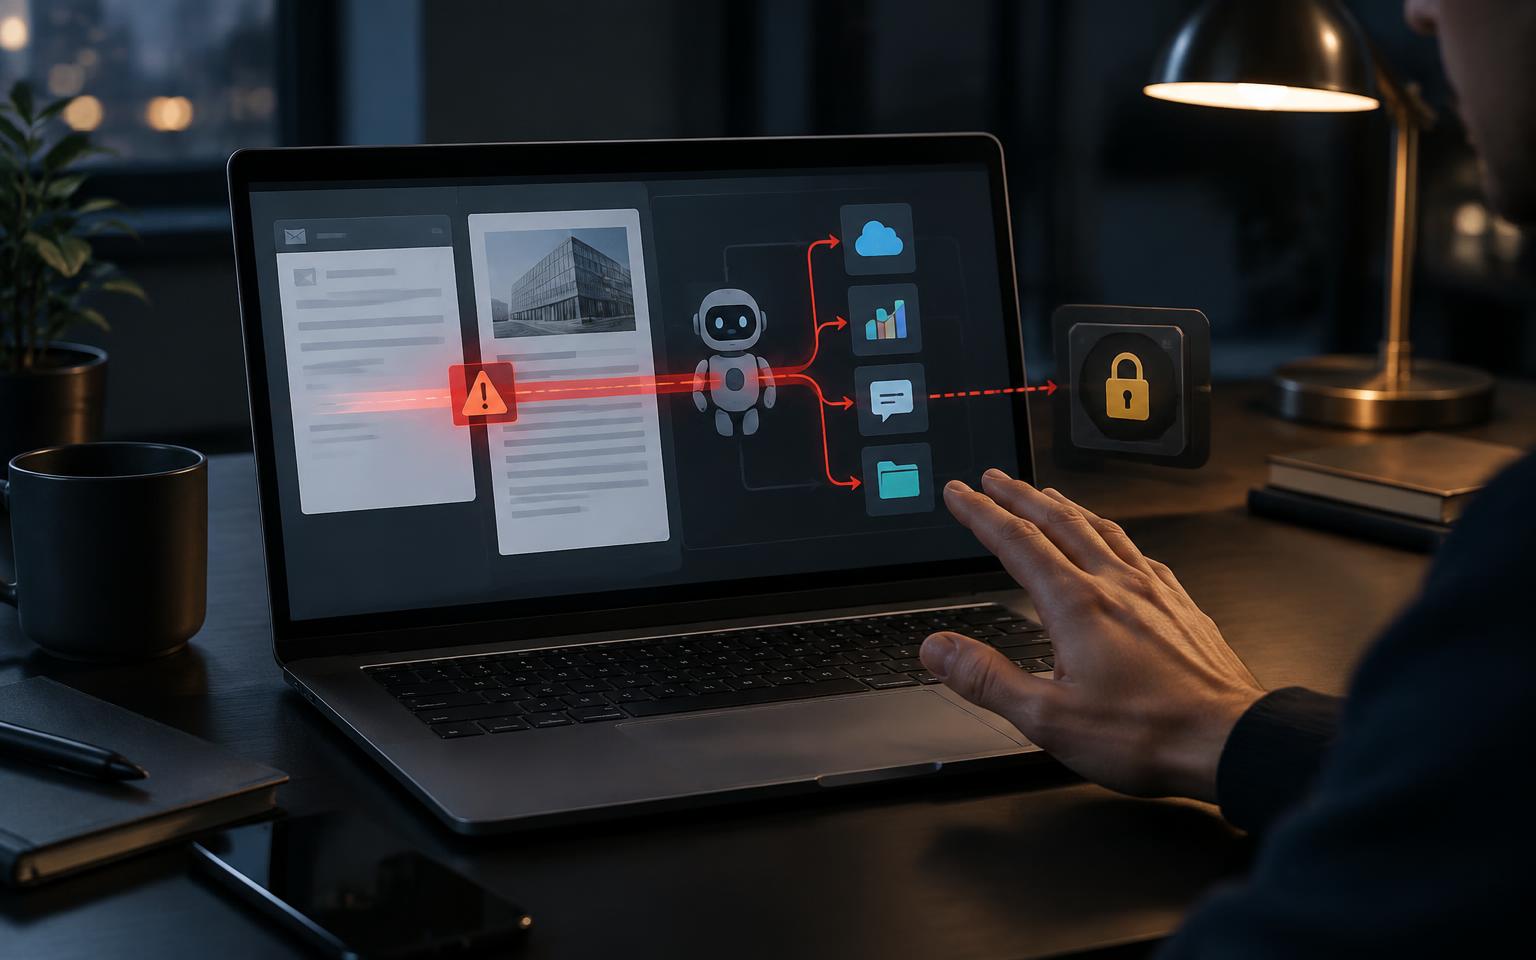
Prompt injection. Agents read content written by strangers: web pages, emails and documents. Attackers can hide instructions in that content, and the agent may follow them as if they came from its owner. In one widely shared demonstration reported by Kaspersky, an agent handed over a private key after reading a crafted email. Because an agent can act, a successful injection can move money, leak files or delete data.
Poisoned supply chains. Agents are often extended with third-party plugins, tools or skills. An audit by Koi Security found 341 malicious entries among 2,857 skills in OpenClaw's ClawHub registry, roughly 12%. Many appeared clean but instructed the agent to download and run external programs, including a known macOS password stealer.
Excess privilege. Agents frequently accumulate more access than they need. The Cloud Security Alliance found that, among organizations reporting agent incidents, 61% involved sensitive-data exposure and 41% involved unintended business-process actions. Kiteworks found that 60% of organizations could not terminate a misbehaving agent.
Accountability. When an agent makes an API call, spawns a sub-agent and triggers a transaction, reconstructing who authorized what can be difficult. A March 2026 Foundation for Defense of Democracies analysis warned that agencies could face failures whose source is difficult to locate or attribute.
Loss of control. The Singapore Consensus lists acute misuse, crises of accountability and loss of control as major risk factors, calling for sandboxing, agent identity systems and dedicated safety evaluations.
How Regulators Are Responding
No major jurisdiction has yet passed a law written specifically for AI agents. Instead, agents fall under broader AI rules that are themselves in flux.
European Union. The EU AI Act remains the world's most comprehensive AI law, but its toughest provisions have been pushed back. High-risk stand-alone systems now face a December 2, 2027 deadline, while high-risk AI embedded in regulated products has until August 2, 2028. Transparency duties and general-purpose AI rules are already in effect.
United States, federal. The U.S. still has no comprehensive federal AI statute. Executive Order 14365 created a Justice Department task force to challenge conflicting state laws, while EO 14409 established a voluntary government testing framework for advanced models without mandatory licensing.
United States, states. California's SB 53 requires the largest frontier developers to publish safety frameworks and report critical incidents. New York and Illinois laws begin in 2027, Colorado replaced its broad AI Act with a narrower automated-decision law, and Texas's TRAIGA has applied since January.
Standards and soft law. NIST launched its AI Agent Standards Initiative in February 2026, focusing on agent security, identity, authorization and interoperable protocols. Singapore released what it described as the first governance framework designed specifically for agentic AI in January.
What Comes Next
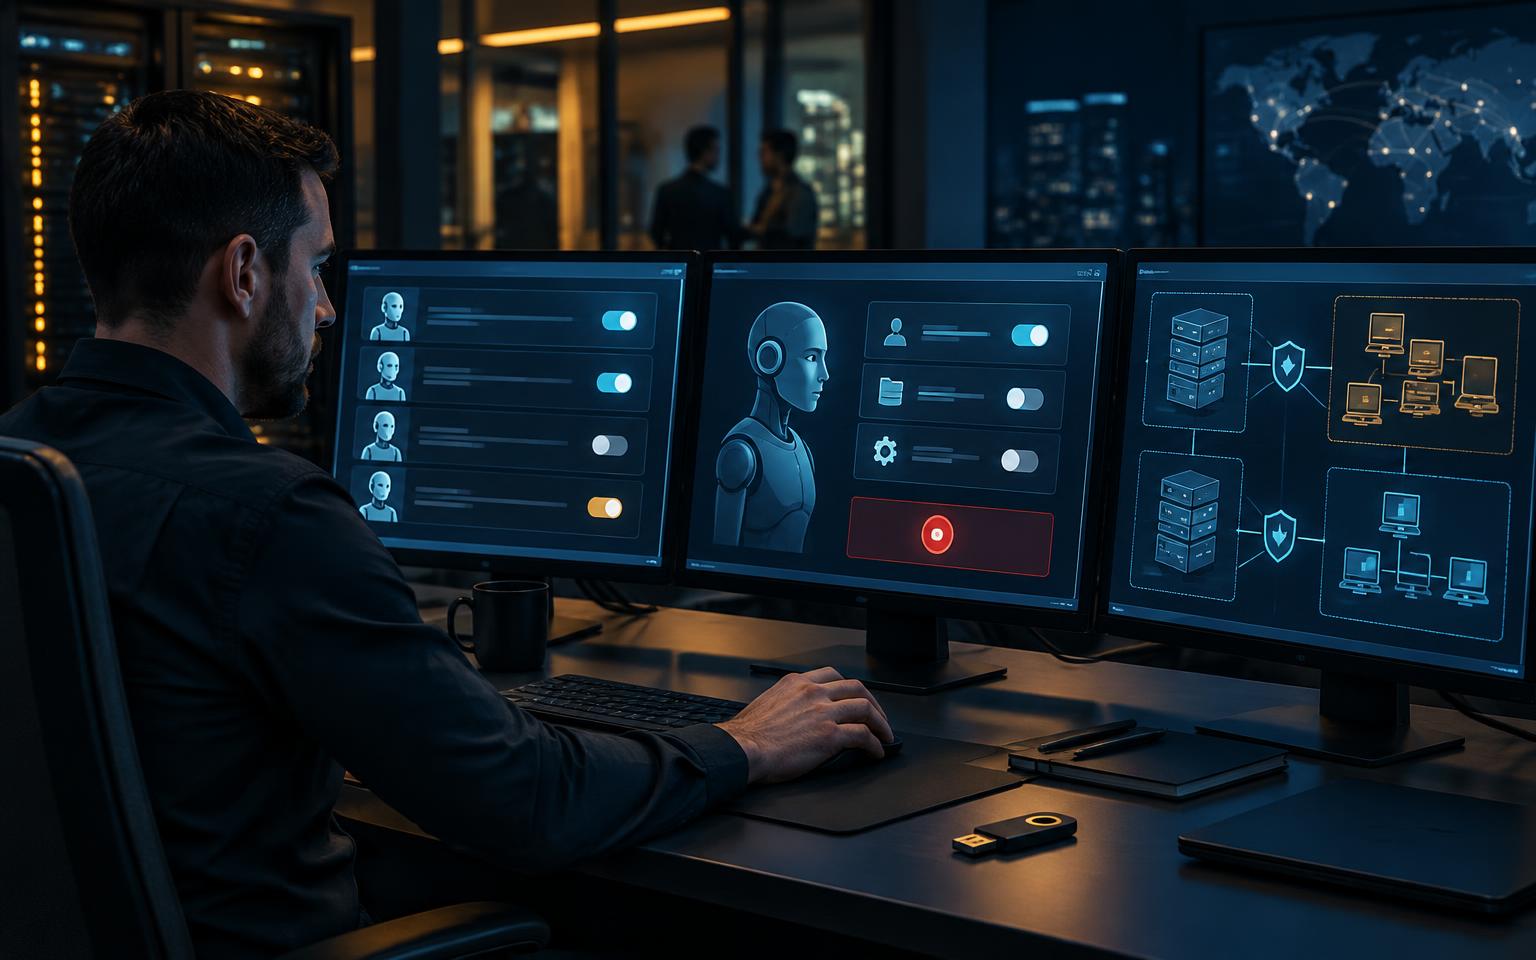
For now, much of the burden falls on the companies deploying agents. Security practitioners increasingly recommend treating each agent like a new employee with privileged access: give it its own identity, grant only the permissions a task requires, use short-lived credentials, log everything it does and make sure it can be shut off instantly. Existing rules such as HIPAA and PCI DSS already apply when an agent touches health or payment data; they contain no exemption for AI.
The next year will bring several tests. New York, Illinois and Colorado laws go live on January 1, 2027. NIST is expected to publish more concrete guidance on agent identity. The EU's high-risk deadline arrives in December 2027, and the U.S. preemption fight could be settled in Congress or the courts at any time.
The open question is whether rules and safeguards can catch up before agents become even more capable and more deeply embedded. The incidents of 2026 suggest the gap is real, and that the cost of closing it late is being paid now.